# Account linking with OAuth
The *OAuth linking* type supports two industry standard OAuth 2.0 flows, the *implicit*
and *authorization* code flows.
In the implicit code flow, Google opens your authorization endpoint in the user's
browser. After successful sign in, you return a long-lived access token to Google.
This access token is now included in every request sent from the Assistant to
your Action.
In the authorization code flow, you need two endpoints:
- The *authorization* endpoint, which is responsible for presenting the sign-in UI to your users that aren't already signed in and recording consent to the requested access in the form of a short-lived authorization code.
- The *token exchange* endpoint, which is responsible for two types of exchanges:
1. Exchanges an authorization code for a long-lived refresh token and a short-lived access token. This exchange happens when the user goes through the account linking flow.
2. Exchanges a long-lived refresh token for a short-lived access token. This exchange happens when Google needs a new access token because the one it had expired.
Although the implicit code flow is simpler to implement, Google recommends that
access tokens issued using the implicit flow never expire, because using token
expiration with the implicit flow forces the user to link their account again.
If you need token expiration for security reasons, you should strongly consider
using the auth code flow instead.
> [!NOTE]
> **Note:** Please choose which OAuth 2.0 flow you want to implement. If needed, the content of this guide reloads to adapt to your choice.
## Implement OAuth account linking
> [!NOTE]
> **Note:** If you're implementing account linking to handle financial information, note that additional policies may apply to your Action. It can take us up to six weeks to review an Action with account linking for financial information, so factor that time in when planning your release schedule. To ease the review process, make sure you comply with the [financial services policies](https://developers.google.com/assistant/console/policies/general-policies#financial_services) before submitting your Action for review.
### Configure the project
To configure your project to use OAuth linking, follow these steps:
1. Open the Actions Console and select the project you want to use.
2. Click the **Develop** tab and choose **Account linking**.
3. Enable the switch next to **Account linking**.
4. In the **Account creation** section, select **No, I only want to allow account creation on my website**.
5. In **Linking type** , select **OAuth** and **Implicit**.
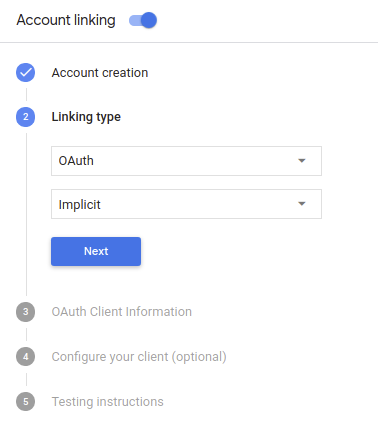
6. In **Client Information**:
- Assign a value to **Client ID issued by your Actions to Google** to identify requests coming from Google.
- Insert the URLs for your Authorization and Token Exchange endpoints.
> [!NOTE]
> **Note:** If you want your client ID to be sent as a base64 encoded string, click the drop down arrow next to **Configure your client (optional)** and check the box **Google to transmit clientID and secret via HTTP basic
> auth header**.
6. Click **Save**.
### Implement your OAuth server
To support the OAuth 2.0 implicit flow, your service makes an authorization
endpoint available by HTTPS. This endpoint is responsible for authenticating and
obtaining consent from users for data access. The authorization endpoint
presents a sign-in UI to your users that aren't already signed in and records
consent to the requested access.
When your Action needs to call one of your service's authorized APIs, Google uses
this endpoint to get permission from your users to call these APIs on their
behalf.
A typical OAuth 2.0 implicit flow session initiated by Google has the
following flow:
1. Google opens your authorization endpoint in the user's browser. The user signs in if not signed in already, and grants Google permission to access their data with your API if they haven't already granted permission.
2. Your service creates an *access token* and returns it to Google by redirecting the user's browser back to Google with the access token attached to the request.
3. Google calls your service's APIs, and attaches the access token with each request. Your service verifies that the access token grants Google authorization to access the API and then completes the API call.
#### Handle authorization requests
When your Action needs to perform account linking via an OAuth 2.0 implicit flow,
Google sends the user to your authorization endpoint with a request that includes
the following parameters:
| Authorization endpoint parameters ||
|---|---|
| `client_id` | The client ID you assigned to Google. |
| `redirect_uri` | The URL to which you send the response to this request. |
| `state` | A bookkeeping value that is passed back to Google unchanged in the redirect URI. |
| `response_type` | The type of value to return in the response. For the OAuth 2.0 implicit flow, the response type is always `token`. |
For example, if your authorization endpoint is available at `https://myservice.example.com/auth`,
a request might look like:
```
GET https://myservice.example.com/auth?client_id=GOOGLE_CLIENT_ID&redirect_uri=REDIRECT_URI&state=STATE_STRING&response_type=token
```
For your authorization endpoint to handle sign-in requests, do the following steps:
1. Verify the `client_id` and `redirect_uri` values to
prevent granting access to unintended or misconfigured client apps:
- Confirm that the `client_id` matches the client ID you assigned to Google.
- Confirm that the URL specified by the `redirect_uri` parameter has the following form:
```
https://oauth-redirect.googleusercontent.com/r/YOUR_PROJECT_ID
```
YOUR_PROJECT_ID is the ID found on the *Project settings* page of the Actions Console.
2. Check if the user is signed in to your service. If the user isn't signed
in, complete your service's sign-in or sign-up flow.
3. Generate an access token that Google will use to access your API. The
access token can be any string value, but it must uniquely represent the
user and the client the token is for and must not be guessable.
4. Send an HTTP response that redirects the user's browser to the URL
specified by the `redirect_uri` parameter. Include all of the
following parameters in the URL fragment:
- `access_token`: the access token you just generated
- `token_type`: the string `bearer`
- `state`: the unmodified state value from the original request The following is an example of the resulting URL:
```
https://oauth-redirect.googleusercontent.com/r/YOUR_PROJECT_ID#access_token=ACCESS_TOKEN&token_type=bearer&state=STATE_STRING
```
Google's OAuth 2.0 redirect handler will receive the access token and confirm
that the `state` value hasn't changed. After Google has obtained an
access token for your service, Google will attach the token to subsequent calls
to your Action as part of the [AppRequest](https://developers.google.com/assistant/conversational/df-asdk/reference/webhook/rest/Shared.Types/AppRequest#User.FIELDS.access_token).
### Design the voice user interface for the authentication flow
> [!WARNING]
> **Warning:** Don't give users a required account linking prompt at the start of the conversation with your Action. Instead, give unauthenticated users a guest flow to show how your Action works, and then only ask for account linking if it's necessary to proceed. If users are leaving the Action consistently because of account linking issues, Google will not actively promote the Action, which may decrease the Action's user traffic.
>
>
> [!NOTE]
> **Note:** You must use [Actions Builder](https://developers.google.com/assistant/conversational/build#actions_builder) to build an Action that implements account linking.
#### Check if the user is verified and start the account linking flow
1. Open your Actions Builder project in the [Actions Console](https://console.actions.google.com).
2. Create a new scene to start account linking in your Action:
1. Click **Scenes**.
2. Click the **add** (+) icon to add a new scene.
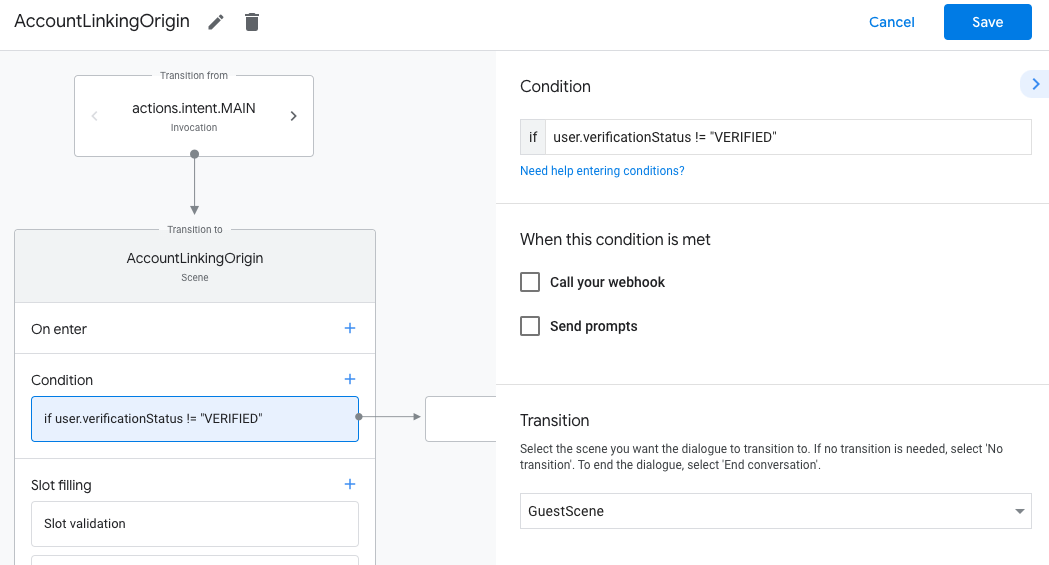
3. In the newly created scene, click the add icon for **Conditions**.
4. Add a condition that checks if the user associated with the conversation is a a verified user. If the check fails, your Action can't perform account linking during the conversation, and should fall back to providing access to functionality that doesn't require account linking.
1. In the `Enter new expression` field under **Condition** , enter the following logic: `user.verificationStatus != "VERIFIED"`
2. Under **Transition**, select a scene that doesn't require account linking or a scene that is the entry point to guest-only functionality.
1. Click the add icon for **Conditions**.
2. Add a condition to trigger an account linking flow if the user doesn't have an associated identity.
1. In the `Enter new expression` field under **Condition** , enter the following logic:: `user.verificationStatus == "VERIFIED"`
2. Under **Transition** , select the **Account Linking** system scene.
3. Click **Save**.
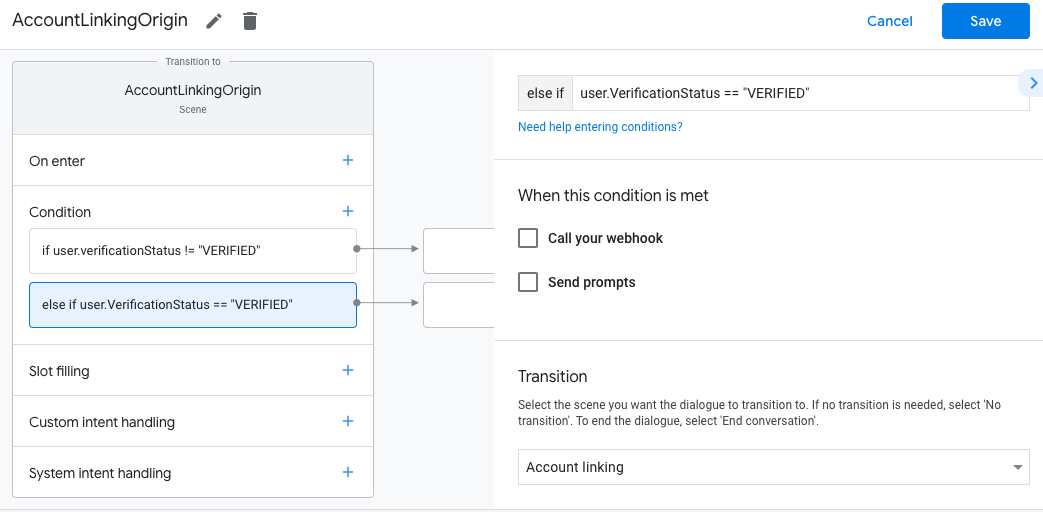
After saving, a new account linking system scene called `_AccountLinking`
is added to your project.
#### Customize the account linking scene
1. Under **Scenes**, select the account linking system scene.
2. Click **Send prompt** and add a short sentence to describe to the user why the Action needs to access their identity (for example "To save your preferences").
3. Click **Save**.
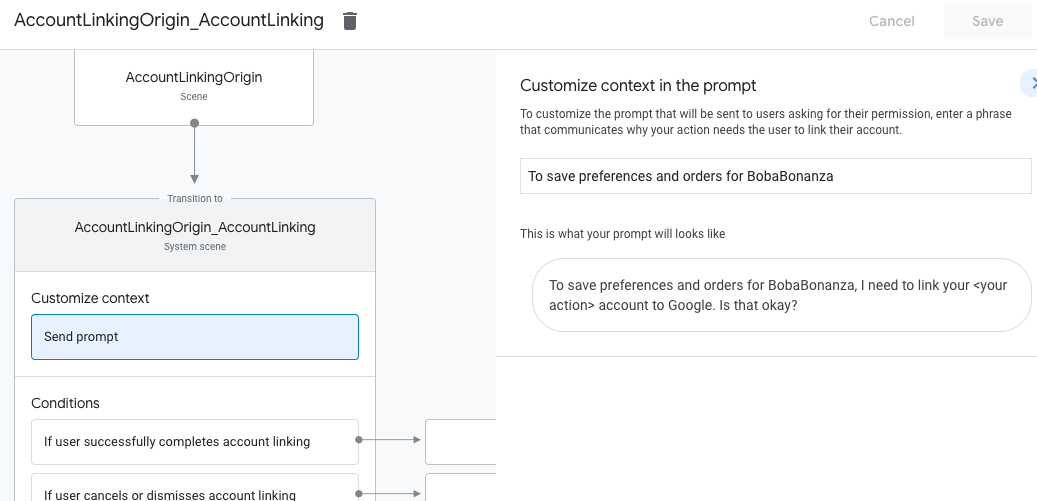
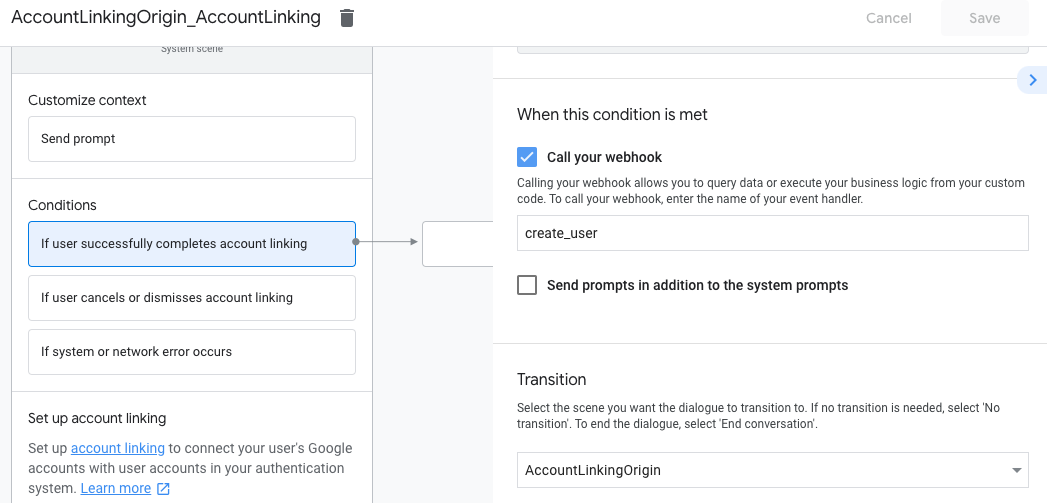
1. Under **Conditions** , click **If user successfully completes account linking**.
2. Configure how the flow should proceed if the user agrees to link their account. For example, call the webhook to process any custom business logic required and transition back to the originating scene.
3. Click **Save**.
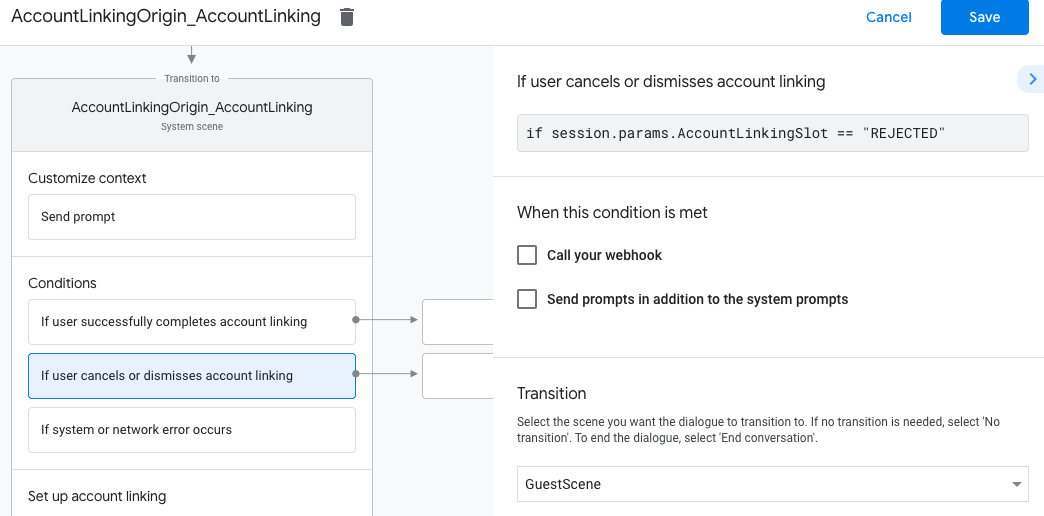
1. Under **Conditions** , click **If user cancels or dismisses account linking**.
2. Configure how the flow should proceed if the user doesn't agree to link their account. For example, send an acknowledging message and redirect to scenes that provide functionality that doesn't require account linking.
3. Click **Save**.
1. Under **Conditions** , click **If system or network error occurs**.
2. Configure how the flow should proceed if the account linking flow can't be completed because of system or network errors. For example, send an acknowledging message and redirect to scenes that provide functionality that doesn't require account linking.
3. Click **Save**.
### Handle data access requests
If the [Assistant request contains an access token](https://developers.google.com/assistant/conversational/reference/rest/Shared.Types/AppRequest#User.FIELDS.access_token),
first check that the access token is valid (and not expired) and then retrieve the associated user account from your database.